
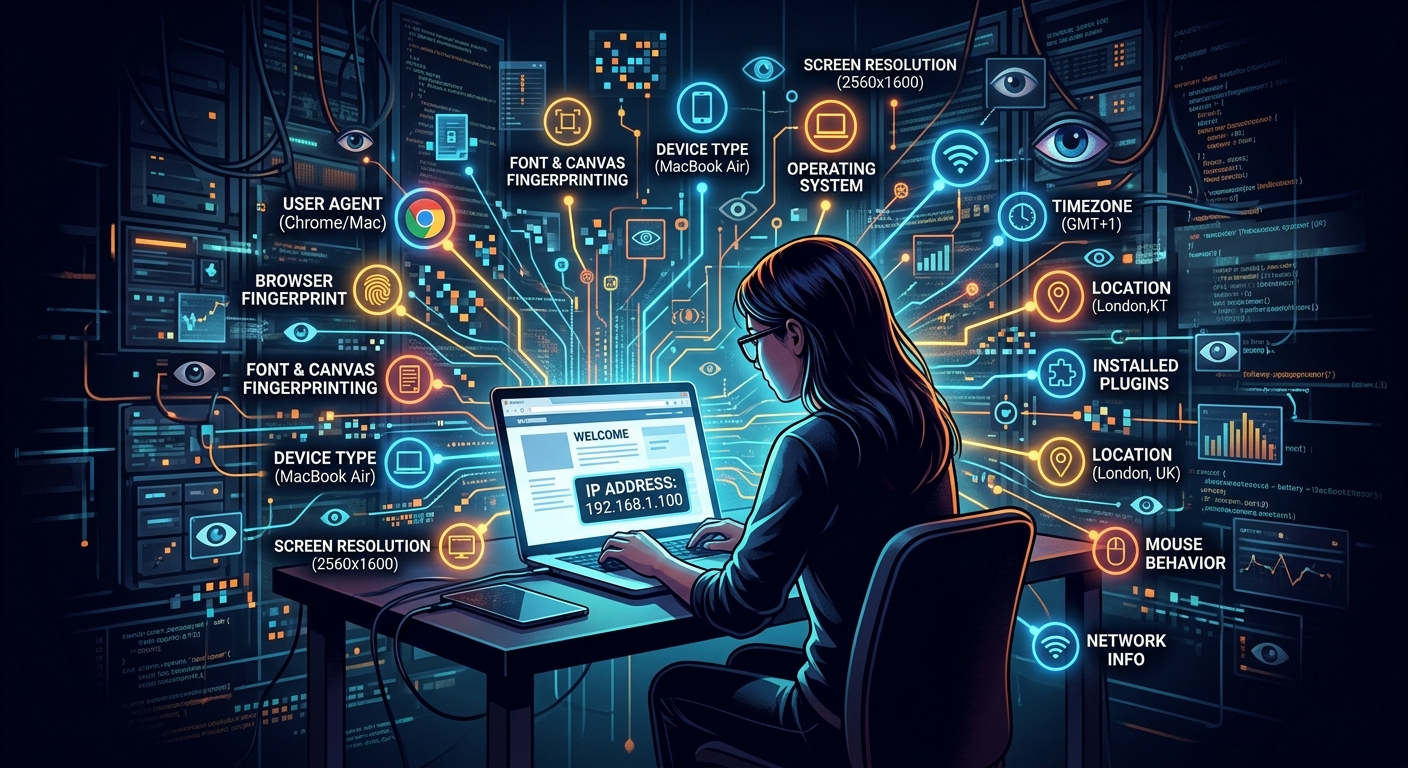
Your IP Address Is Not the Only Thing Websites Use to Track You
Network
IP and DNSDescribes the route and resolver handling the connection.
Device
FingerprintDescribes a stable combination of browser and hardware traits.
Identity
Cookies and emailReconnects sessions to an account or persistent browser state.
You switched on your VPN, watched your IP change, and felt a small rush of privacy satisfaction. But the website you just visited already had a profile on you, built from signals your VPN did nothing to hide. IP masking is a good start. It is nowhere near the finish line.
Privacy Reality Check
- Browser fingerprinting creates a unique device ID from dozens of technical details, no cookies required.
- DNS leaks can hand your full browsing history to your ISP even when a VPN appears to be working.
- Every account you register with your real email address adds a permanent thread back to your real-world identity.
The Many Ways a Website Sees You
Think of online tracking like a forensic investigation. If one clue is removed, investigators do not give up. They look for fingerprints, hair fibers, timestamps, anything that places you at the scene. Websites work the same way. Your IP address is one data point. Remove it and there are still plenty of others waiting to pick up the trail.
Modern ad networks, analytics platforms, and even ordinary websites combine signals constantly. The result is a profile that can follow you across devices, sessions, and browsers. Understanding what those signals are, and how to blunt them, puts that power back in your hands.
Browser Fingerprinting: The Tracker That Needs No Cookie Jar
Every time your browser loads a page, it broadcasts a small autobiography. Screen resolution, installed fonts, graphics card behavior, time zone, language settings, browser version, whether you block ads, the list is long. Individually, none of these facts seem unique. Combined, they form a fingerprint that identifies your specific device with surprising accuracy.
The Electronic Frontier Foundation has demonstrated this clearly. Their browser uniqueness test shows that most users have a configuration rare enough to pick them out of a crowd of millions, without a single cookie being set.
Here is what goes into a typical fingerprint:
- Screen dimensions and color depth
- Installed system fonts, detected via CSS or JavaScript
- Canvas fingerprint, which is how your GPU renders a hidden image
- WebGL renderer and vendor strings
- Audio context behavior caused by subtle hardware-level differences
- Installed browser plugins and their versions
- Time zone and preferred language settings
- Whether cookies and JavaScript are enabled
The countermeasure here is controlled blending in. Browsers like Firefox with strict privacy mode, or Tor Browser, work to make your fingerprint look identical to thousands of other users. Privacy-hardened Chromium forks like Brave use randomization to subtly shift the fingerprint on each session. Disabling JavaScript entirely stops most fingerprinting cold, though it also breaks the majority of modern websites, which makes it a last resort rather than a daily habit.
| Tracking layer | How continuity is created | Focused control |
|---|---|---|
| IP address | A network address groups requests made through the same route. | Change and verify the route with a VPN or Tor when the use case requires it. |
| Browser fingerprint | A combination of fonts, rendering, screen, language, and hardware traits repeats. | Use fingerprint-resistant defaults and avoid unusual one-off customizations. |
| Browser storage | Cookies, local storage, IndexedDB, and service workers retain identifiers. | Partition or clear site data and block unnecessary third-party scripts. |
| Account email | A durable address connects activity to one login identity. | Use aliases or disposable addresses where a permanent identity is unnecessary. |
Tracking Cookies and Their Less-Famous Cousins
Most people know that websites drop cookies to remember them. Fewer realize that cookies are just one of several storage mechanisms that serve the same purpose. Local storage, session storage, IndexedDB, and service workers can all hold persistent identifiers. Advertisers have leaned on these alternatives whenever cookie deletion became popular.
Respawning is a known trick. A site stores your ID in a cookie and also in local storage. You delete the cookie. The next visit, the site reads the local storage entry and rewrites the cookie. You are back to square one without knowing it.
Third-party cookies, long the backbone of ad network tracking, have been in retreat. Major browsers have moved to block them by default. But first-party cookies placed by the site you actually visit still work fine, and tracking companies have adapted by moving their code into the first-party context through a technique called CNAME cloaking.
The practical countermeasure is layered. Use a browser that blocks third-party cookies and partitions storage between sites. Firefox and Brave both do this by default. A browser extension that clears cookies and site data on tab close adds another layer. Combined with a fingerprint-resistant browser, this removes most cookie-based tracking from your daily sessions.
- 1. Network signal changesThe VPN replaces the visible IP for the destination.
- 2. Browser signal remainsFingerprint traits and stored identifiers continue to match earlier visits.
- 3. Identity is suppliedA login or email address joins the session to an account.
- 4. Profiles reconnectThe service can associate the new route with the existing browser or account record.
DNS Leaks: The Privacy Gap Your VPN May Be Hiding From You
Your VPN encrypts the traffic between your device and the VPN server. What it may not do is route every DNS query through that encrypted tunnel. DNS queries are the lookups your device makes to translate a domain name into an IP address. If those queries skip the VPN and go directly to your ISP's DNS servers, your ISP can see every domain you visit, regardless of what your displayed IP address shows.
This gap is called a DNS leak, and it is more common than most VPN users expect. DNS over HTTPS was introduced to encrypt these lookups at the protocol level, making them unreadable to anyone monitoring the connection between your device and the resolver.
Testing for a DNS leak is straightforward. Run a VPN leak test before and after activating your VPN. If the test shows your real ISP's name servers after the VPN is on, you have a leak. The fix depends on your VPN client. Good VPN software includes a built-in DNS leak prevention setting. If yours does not have one, you can manually configure your device to use an encrypted DNS resolver independent of what your ISP provides, which closes the gap regardless of which VPN you use.
Email Addresses and the Identity Thread That Never Breaks
Every privacy precaution you take in the browser can be undone in seconds by signing up for a service with your real email address. Email is a persistent, real-world identity anchor. It connects your activity on a platform to your name, phone number, purchase history, and sometimes your physical address. Once a company has your real inbox, it can share or sell that data to data brokers, and those brokers can link it to profiles built from dozens of other sources.
The pattern is familiar. You visit a site once to grab a free download or read a gated article. The form asks for your email. You hand it over. Now that address sits in a CRM, possibly linked to your browsing behavior via a tracking pixel embedded in the confirmation email sent immediately after you register.
The cleanest solution is using a disposable address for any registration that does not need to be permanent. A fake email gives you a working inbox for confirmations without attaching your real identity to the account. If the service turns out to be worth keeping, you can update to your real address later. If it floods you with spam, you simply abandon the disposable inbox and nothing follows you out.
How Each Tracking Layer Stacks Up Against Its Fix
Tracking Methods Compared by What They Expose and What Counters Them
| Tracking Method | What It Exposes | Effective Countermeasure |
|---|---|---|
| Browser Fingerprinting | Device identity across sessions, without cookies | Fingerprint-resistant browser (Brave, Firefox, Tor Browser) |
| Tracking Cookies and Storage | Browsing history, behavior, and cross-site identity | Block third-party cookies, clear all storage on exit |
| DNS Leaks | Every domain you visit, despite an active VPN | VPN with DNS leak protection, encrypted DNS resolver |
| Email Harvesting | Real-world identity and connected data broker profiles | Disposable address for non-essential sign-ups |
| IP Address | General location and ISP | VPN or Tor, combined with the measures above |
What this comparison cannot prove
A reduced fingerprint or changed IP makes correlation harder, not impossible. Logging in, reusing an email, or restoring synchronized browser data can reconnect the session immediately.
Building Habits That Actually Reduce Your Exposure
Each tracking method above has a fix. None of them require deep technical knowledge. The gap between a closely tracked user and a much harder to track one comes down to consistent habits applied across every layer where your identity is at risk.
- Use Firefox with enhanced tracking protection set to Strict, or switch to Brave for fingerprint resistance built in by default.
- Enable your VPN's built-in DNS leak protection, or run a leak test to confirm it is working before trusting the connection.
- Set your browser to clear cookies and site data when it closes, and pair it with a content blocker that targets third-party scripts and tracking pixels.
- Use a disposable email address for any registration you are not committed to, including free trials, one-time downloads, and gated content.
- Treat your real email address the way you treat a phone number. Share it selectively, and use per-service aliases for accounts that genuinely matter to you.
The Threads That Outlast Your IP Address
Focusing entirely on your IP address is like locking the front door and leaving every window open. Websites, advertisers, and data brokers do not need your IP to identify you. They build a composite picture from signals that are harder to notice and easier to underestimate.
Your browser's technical quirks, the cookies that survive a VPN toggle, the DNS queries slipping outside the encrypted tunnel, and the email address you typed into a form years ago, each one is a thread in a tapestry that describes you in precise detail. Pull any one thread and the others stay intact.
Privacy is not a single tool. It is a set of consistent choices made at every layer where your identity is at risk. Start with the fixes that cost you the least friction and work outward from there. Each layer you close makes the next tracking method that much less useful to anyone building a profile on you without your knowledge or consent.
Continue this privacy investigation