
How to Check for DNS Leaks and Keep Your VPN Actually Private
Baseline
VPN offRecords the home ISP, resolver, and address families before the test.
Comparison
VPN onShows whether the public IP and resolver move to the intended path.
Failure clue
Mixed ownershipA VPN IP beside an ISP resolver indicates split handling that needs review.
Your VPN is connected. The status bar shows a green light. But your internet service provider may still be logging the name of every website you visit. This is not a rare edge case reserved for misconfigured enterprise setups. It happens on ordinary home connections, and most people running a VPN right now have no way of knowing whether it applies to them. The problem has a name: a DNS leak. It is one part of what your IP address leaks and which privacy tools close the gaps.
What You Need to Know
A DNS leak sends your name-resolution requests outside your VPN tunnel, handing your browsing history back to your ISP even when your traffic looks encrypted. Testing for one takes about 60 seconds and requires no technical skill. Fixing it usually comes down to a single setting. Knowing how to do both is what separates a VPN that feels private from one that actually delivers on that promise.
The Part of Every Web Request Your VPN Might Be Skipping
Every time you load a website, your device runs a quiet background task before the page appears. It takes the human-readable domain name you typed and converts it into a numerical IP address your browser can connect to. That conversion is handled by a Domain Name System server, and the request your device sends to that server carries the name of every site you want to reach.
Under normal conditions, without any VPN running, your ISP controls that DNS server. It receives your queries, resolves them, and can log them. That log is a near-complete record of your browsing activity, separate from the content of any pages you visit. The domain names alone tell a detailed story: health conditions researched, news sites read, services compared.
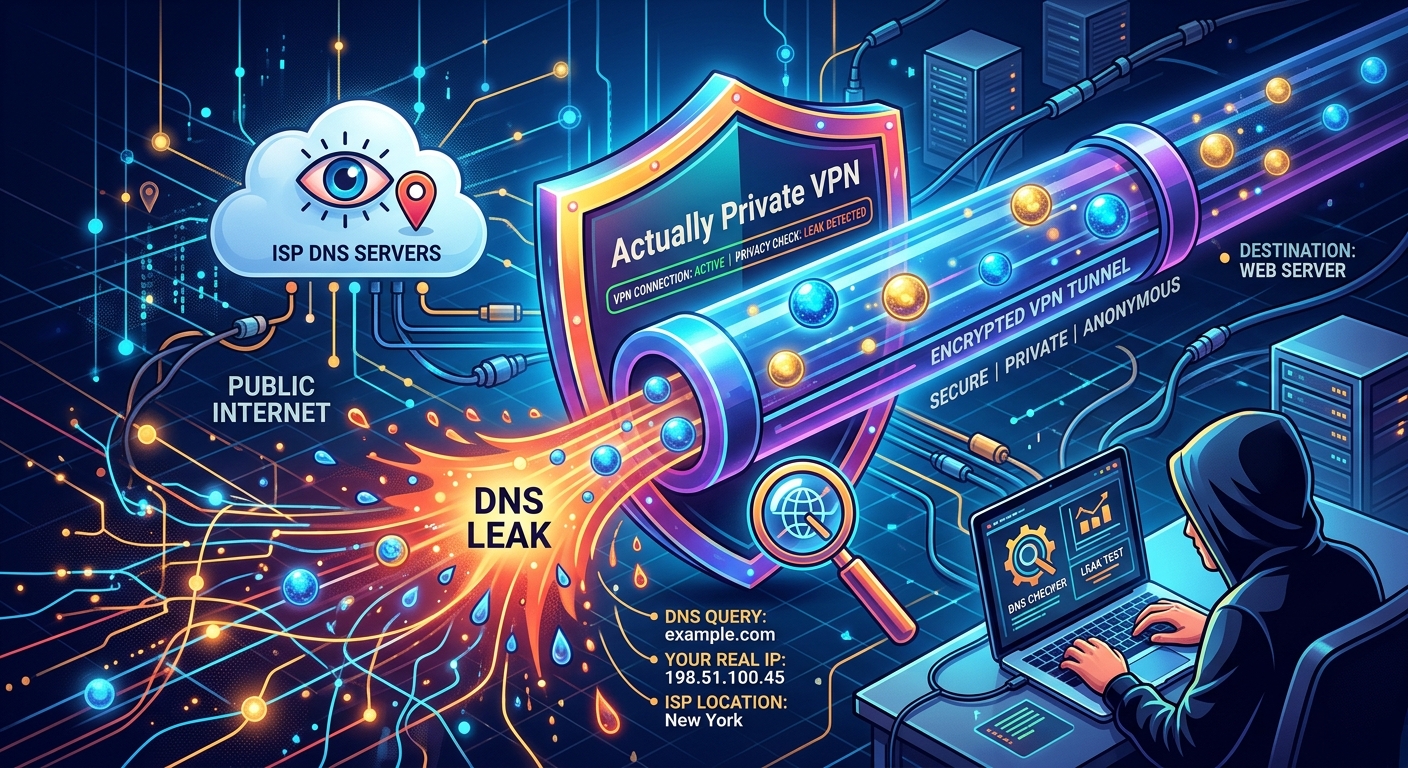
A VPN is supposed to intercept those DNS queries along with everything else and route them through an encrypted tunnel to a server run by the VPN provider. Your ISP sees only the encrypted tunnel, not the names inside it. A DNS leak is what happens when the arrangement breaks and those queries travel outside the tunnel anyway, in plain text, directly to your ISP's resolver.
| Leak path | Evidence to capture | Focused correction |
|---|---|---|
| System resolver fallback | The ISP resolver remains visible after the VPN connects. | Enable the client's DNS protection or bind DNS to the tunnel. |
| IPv6 bypass | IPv4 follows the tunnel while IPv6 or its resolver uses the ISP. | Use a VPN with IPv6 support or disable IPv6 only when that limitation is understood. |
| Split tunneling | One browser or process uses the direct route while others use the VPN. | Place the affected process inside the tunnel or document the intended exception. |
| Reconnect failure | The resolver changes during a tunnel drop and does not return afterward. | Use a kill switch with DNS binding and repeat a controlled reconnect test. |
Why Your Connection Can Leak Even With a VPN Active
The causes are more common than most VPN marketing materials admit.
Windows has a built-in feature called Smart Multi-Homed Name Resolution. It is designed to speed up lookups by sending DNS queries to several servers at once and accepting whichever answer arrives first. This includes your ISP's server. The feature stays active even when a VPN is connected, and some VPN clients do not block it.
IPv6 is another weak point. A large number of VPNs encrypt only IPv4 traffic. If your router and ISP support IPv6, and many do now, DNS requests can leave your device over an unprotected IPv6 path that bypasses the tunnel entirely. Your queries arrive at your ISP's resolver just as if the VPN were switched off.
Careless split-tunneling settings create similar gaps. Split tunneling lets you decide which apps use the VPN and which connect directly. If a browser or system process falls outside the tunnel, it falls back to your default DNS server, which belongs to your ISP.
Some VPN clients also default to using system DNS rather than their own resolver, particularly on mobile devices or on networks where the VPN connection drops briefly and reconnects without properly re-establishing DNS routing. The reconnection looks seamless. The leak does not announce itself.
- 1. Test without the VPNRecord public IP, ISP, resolver names, and IPv4 or IPv6 results.
- 2. Connect the VPNWait for the tunnel and its DNS settings to settle before opening the test.
- 3. Run the same checksCompare the public network, resolver owner, DNS path, and WebRTC output.
- 4. Reconnect and verifyApply one correction, reconnect, and repeat the exact test.
How to Check Which DNS Server Your Device Is Actually Using
Testing is the only way to know for certain. The method is direct: find out which DNS server is handling your queries while your VPN is connected, then check whether that server belongs to your VPN provider or your ISP.
The most practical approach is to use a check the tunnel for IP, DNS, and WebRTC leaks while your VPN is connected. Compare the detected network and resolver details with your ISP baseline. If the IP address or hostname in the result belongs to your ISP rather than your VPN provider, your DNS requests are leaking outside the tunnel.
What you want to see is a server associated with your VPN provider, or at minimum a public privacy-focused resolver that has no connection to your ISP. What you do not want to see is your ISP's server name or an IP block that traces back to your broadband provider's infrastructure.
Run the test twice. First with the VPN off, to establish a baseline showing your ISP's DNS server. Then again with the VPN on. If both results return the same server, your VPN is not protecting your DNS traffic at all, regardless of what the connection status indicator says.
Fixing the Leak Without Replacing Your VPN
In many cases, a DNS leak is fixable without switching providers or reinstalling anything. The following steps address the most common causes:
- Enable the DNS leak protection setting in your VPN client. Most major clients include this option, sometimes labeled as "DNS leak prevention" or "prevent DNS leaks." It tells the client to block any DNS query that tries to exit the tunnel and reroutes it through the VPN's resolver.
- Disable IPv6 on your network adapter if your VPN does not support it. This stops queries from escaping over an unprotected IPv6 path. On Windows, the option is in network adapter properties. On macOS, it can be set per-network in System Settings under your active connection.
- Set your DNS server manually to a privacy-focused resolver. Pointing your device to a non-ISP resolver does not by itself seal the tunnel, but combined with correct VPN configuration it gives you a known, non-ISP server handling any fallback requests.
- Turn on DNS over HTTPS in your browser. Firefox and Chrome both support this natively in their privacy settings. When active, DNS queries from the browser are encrypted at the application layer before leaving your device. The DoH standard, formalized by the IETF, was developed to address precisely this kind of plaintext exposure.
- Disable Smart Multi-Homed Name Resolution on Windows. This is done through Group Policy settings or the registry. It prevents Windows from sending DNS queries to multiple servers simultaneously, which closes one of the most common paths for leaks on the platform.
What this comparison cannot prove
Resolver ownership is evidence about the DNS path. It does not prove a provider's logging behavior, and one clean run does not prove the route stays protected during reconnects.
What a Genuinely Privacy-Protective VPN Handles for You
When you compare VPNs by protocol, policy, and use case, pay close attention to DNS handling. Some route queries through their own resolvers by default. Others rely on whatever DNS settings your device already has configured. A few specific features tell you whether a provider has actually thought through this problem:
- Private DNS resolvers operated by the provider. This keeps your browsing queries from passing through any third-party infrastructure outside the VPN relationship itself.
- A specific no-log DNS policy. This is separate from a general no-logs claim. A provider can avoid logging connection metadata while still recording which domains you queried. Look for providers that explicitly address DNS logging in their privacy policy.
- A kill switch that binds DNS to the tunnel. If the VPN connection drops, the kill switch cuts internet access rather than failing open and reverting to your ISP's DNS. The binding ensures DNS does not outlast the connection.
- DNS over HTTPS or DNS over TLS for communication with the resolver. This encrypts the query between your device and the VPN's own server, protecting against interception even within the tunnel.
- Encouragement to run leak tests. Providers that point you toward testing tools and publish their expected resolver results are more credible than those that treat the topic as irrelevant or advanced.
Where the Gap Between Encrypted Traffic and Private Browsing Actually Lives
Traffic encryption and DNS privacy are two different things. A VPN that encrypts your data packets but sends your DNS queries in the clear is like mailing a sealed letter but writing every destination address in large print on the outside. The contents are hidden. The destination is not.
Your ISP receives your DNS queries and can see the domain names. That is enough to build a detailed picture of your browsing habits, even without reading a single byte of your actual traffic. In some countries, ISPs are required to retain this data for a set period. In others, they sell aggregated data to advertisers. Even where neither practice applies, the information exists and is accessible to the provider and anyone who compels them to share it.
A DNS leak does not break your VPN entirely. Your IP address is still masked from the sites you visit. Your traffic is still encrypted in transit. But the browsing history you were trying to protect is visible to exactly the party you were trying to keep it from.
Running the test takes under a minute. Fixing most leaks takes five minutes after that. The distance between a VPN that feels private and one that actually is comes down to that short window of verification, and whether you have ever taken the time to close it.
Continue this privacy investigation