
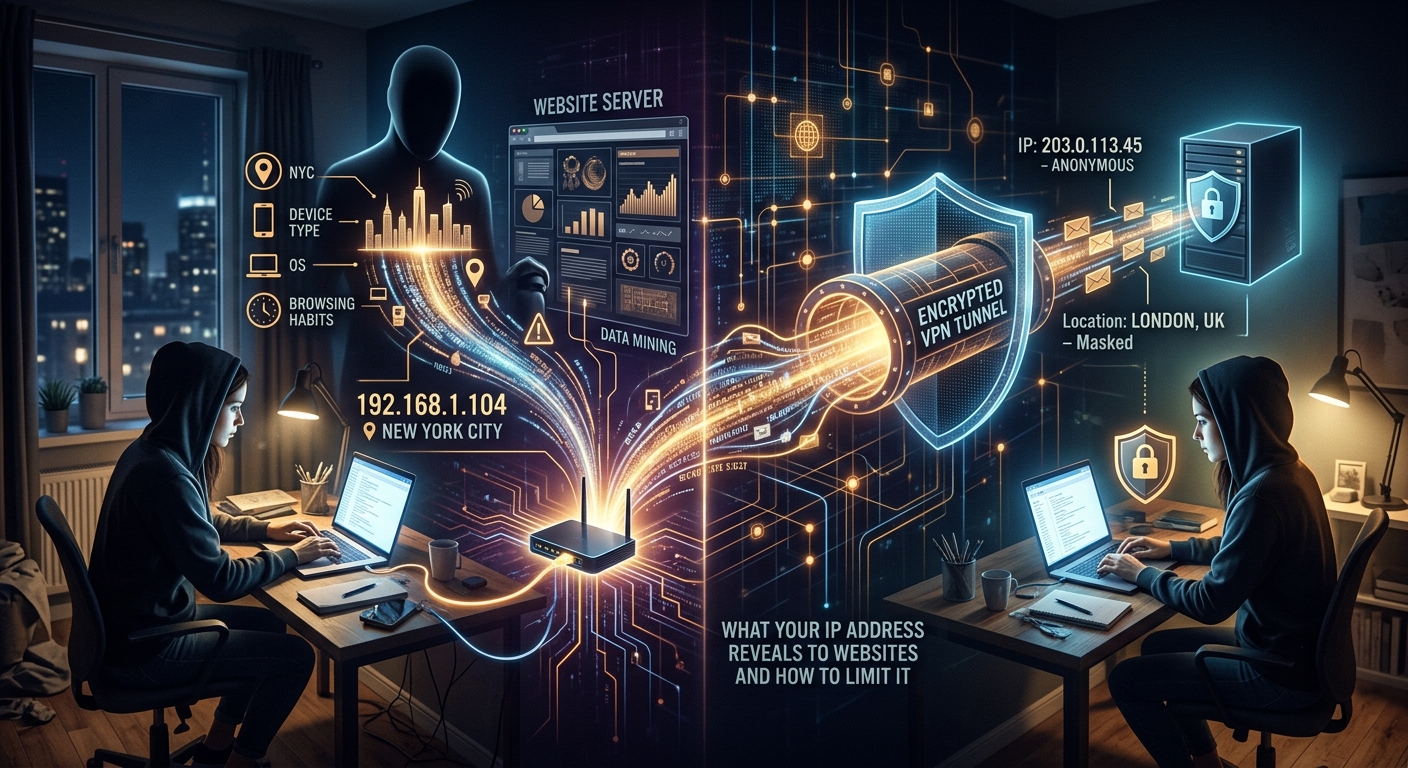
What Your IP Address Reveals to Websites and How to Limit It
Directly visible
IP addressRequired so the server can return data to the connection.
Database lookup
ISP and regionDerived from routing, registration, and geolocation datasets.
Combined profile
IP plus browserBecomes more identifying when joined to cookies, fingerprints, or logins.
Every website you visit knows something about you before you type a single character. That something is your IP address. It arrives with every request your browser sends, and the server on the other end reads it the moment the connection forms. Most people assume it reveals only a vague sense of their location. The reality is more specific, and once IP data gets layered with other signals, the picture that emerges can surprise you.
At a GlanceEach time you load a webpage, your device sends an IP address that can expose your approximate city, the name of your internet provider, and a consistent marker that ad networks use to build patterns over time. Each of those exposures has a practical counter. This piece walks through what leaks, explains how websites use that data, and pairs every risk with a step you can act on today.
The Information Hidden Inside Every IP Address
An IP address is a numerical label assigned to every device that connects to the internet. Under the IPv4 specification, the format is four groups of numbers separated by dots, like 203.0.113.47. That number is not random. Your internet service provider issues it, and it maps back to a specific block of addresses tied to a geographic region and an organization name.
Websites do not need to ask where you are. The address carries that context automatically. When your browser requests a page, it sends a data packet with the destination address of the server and your own IP as the return address. The server cannot send content back without it. There is no way to load a page without sharing your IP. This is simply how the internet routes traffic at a foundational level.
What makes this worth paying attention to is that the IP address is logged by default. Every web server keeps access logs. Your IP appears in those logs alongside the timestamp, the page you requested, and your browser's user-agent string. Even pages you visit for a few seconds have a record of your address.
Location Exposure: How Precise Is It Really?
Commercial databases map IP address ranges to physical regions. Companies license this data, update it continuously, and make it available through lookup services. The result is that a website can run a geolocation query against your IP in milliseconds and get back a city name, a state or region, a country, and sometimes a postal area.
Country-level accuracy runs above 99 percent for most commercial databases. City-level accuracy varies more, but in practice it lands within 25 to 50 miles of your actual location the majority of the time. If you live in a mid-sized city, a website checking your IP most likely knows your city by name. It almost certainly knows your country and region with high confidence.
ZIP code accuracy is the least reliable tier. If your ISP assigned your address block to a regional hub far from your neighborhood, the lookup may return the hub city rather than yours. That margin of error does not make you anonymous, though. The site still has your city, your region, and your ISP name. That is enough for targeted advertising, geo-restricted content enforcement, and demographic profiling without you providing a single piece of explicit data.
Your Internet Provider's Name Is Part of the Package
IP address blocks are registered to organizations and publicly listed in databases run by regional internet registries. When you connect through a home broadband plan, your IP exposes the name of that provider. When you connect through a mobile carrier, the carrier's name appears. Corporate networks often reveal the company name directly in the lookup result.
This piece of information feeds into more than most people expect. Ad platforms treat ISP names as a targeting signal. A household connecting through a rural provider gets placed in different audience segments than one connecting through a large cable company in a metropolitan area. Fraud detection systems use ISP data to flag unusual patterns, like an account logging in from a residential address in one country and a datacenter address in another within a few minutes.
Your ISP also occupies a position of structural visibility. The IP relationship works in both directions. Destination servers see your IP, but your ISP sees which IPs you are contacting. That means your provider has a log of every domain you visit at the network level, unless you take active steps to encrypt your DNS queries and route your traffic through a separate service.
| Observed field | Reasonable conclusion | Unsupported conclusion |
|---|---|---|
| Public IP | This address handled the observed connection at that time. | A named person was necessarily using the device. |
| ISP or ASN | The address belongs to or is announced through that network. | The network operator owns the visited account or content. |
| Geolocation | A database associates the address block with a broad area. | The device was at an exact home or street location. |
| Browser fingerprint | The browser configuration may be distinguishable and repeatable. | The fingerprint alone establishes a legal identity. |
Tracking Gets More Powerful When IP Data Is Combined
An IP address in isolation has real limits as a tracking tool. It changes when you restart your router or switch networks. It is shared across everyone in a household. It does not identify a single person the way a name or email address does. Advertisers and trackers know this, which is why they rarely rely on IP alone.
The power comes from combining your IP with other signals. Websites pair it with cookies, session tokens, login identifiers, and browser fingerprints. A browser fingerprint is a collection of details your browser transmits automatically: screen resolution, installed system fonts, language settings, browser version, and the list of active plugins. Together, these details form a profile that is often unique enough to identify your device even after you clear your cookies.
When a tracking pixel from an ad network loads on a webpage, that network logs your IP and matches it to whatever cookie or fingerprint it already holds for your browser. If you visit another site in that same ad network, the log entries get linked. Over weeks and months, the network builds a behavioral profile tied to your browsing patterns. Your IP serves as the anchor that keeps those entries connected across sessions, even when other identifiers change.
- 1. Connection arrivesThe server records the public IP, time, requested resource, and user agent.
- 2. Network data is addedRouting and geolocation sources associate the address with an ASN, provider, and region.
- 3. Browser signals joinCookies, login state, and fingerprint traits connect requests across sessions.
- 4. A profile is inferredThe service groups behavior while uncertainty about the actual person remains.
Hiding Your IP Is Only One Layer of Protection
Masking your IP address is a meaningful and practical step. A VPN routes your traffic through a server in a different location, so every website you visit sees the server's IP rather than yours. The geolocation lookup returns the server's city. The ISP name belongs to the VPN provider. Tracking pixels log an IP that cannot be reliably connected to your household or your browsing history.
That protection has genuine value. But it does not address everything. A VPN hides your IP from websites while leaving your browsing visible to the VPN provider itself. Browser fingerprinting operates independently of your IP address. Cookies set before you connected to a VPN may still identify your browser session. DNS queries can leak outside the VPN tunnel on misconfigured clients, exposing the domains you visit to your real ISP even while the VPN is active.
These gaps are precisely where reading a thorough online privacy guide adds real value. DNS leaks, WebRTC exposure, and fingerprinting are separate problems that sit alongside IP exposure rather than underneath it. Treating IP masking as the complete solution leaves those gaps open and largely unaddressed.
What this comparison cannot prove
An IP result describes a network observation at a specific time. Attribution to a household, account, device, or person requires separate authorized evidence.
A Step-by-Step Plan to Cut What Your IP Gives Away
The steps below are ordered from the simplest to the most thorough. Completing even the first two will meaningfully reduce what you expose during ordinary daily browsing.
- Run an IP address lookup on yourself right now. Note the city, ISP name, and any other data that comes back. That is your current baseline, and it tells you exactly what any website sees the moment you arrive.
- Choose a VPN for the risks that actually apply, then select a provider with a published and audited no-logs policy. Enable it before connecting to any network you do not personally control, starting with public Wi-Fi at coffee shops, airports, and hotels.
- Switch your DNS settings to a provider that supports DNS over HTTPS. This encrypts your domain name requests so your ISP cannot read them in transit. Most modern browsers and operating systems now support this natively in their settings panels.
- Test your browser for WebRTC leaks. Some browsers expose your real IP through WebRTC connections even when a VPN is active. A settings change or browser extension can close this exposure without affecting your general browsing experience.
- Install a content blocker such as uBlock Origin. It prevents third-party tracking scripts and pixels from loading at all, which stops ad networks from logging your IP alongside their cookie and fingerprint data across different sites.
- Use a privacy-focused browser or a hardened browser profile for sensitive browsing sessions. Pairing it with a VPN covers both your IP-level exposure and your fingerprint profile at the same time, addressing two separate tracking vectors in one workflow.
What Actually Stays Private After You Take Action
Once you work through those steps, the exposure landscape shifts noticeably. Websites still receive an IP address with every request, but it belongs to the VPN server. The city in the geolocation result is wherever that server is physically located. The ISP name is the VPN provider's. Tracking pixels log an IP that cannot be reliably traced back to your household.
Your browsing habits become far harder for your internet provider to catalog. DNS queries travel encrypted and bypass your ISP's logging layer. Content blockers prevent the tracking scripts that would have linked your IP to a behavioral profile across dozens of unrelated sites you visit in a single afternoon.
The goal here is not complete invisibility. A determined, well-resourced adversary with access to multiple data streams can still work to connect information. But the realistic threat for most everyday users is not that kind of surveillance. It is passive, automated data harvesting by advertising networks, data brokers, and analytics platforms that monetize aggregated browsing behavior at scale.
Against that specific threat, these steps are genuinely effective. Your IP address leaks real and specific information about where you are and who provides your internet service. It acts as an anchor for cross-site tracking when combined with browser signals you may not realize you are broadcasting. It is also one of the more controllable pieces of the puzzle. The steps above require no deep technical background and no significant expense. They require knowing what the problem is, understanding why it matters, and deciding to do something about it.
Continue this privacy investigation